Sigma - AI Co-Pilot for AML Case Management
Sector
Financial compliance
Market
B2B
What I did
User research, Product design
Year
2026

The problem
Bank compliance teams work inside a high-stakes, high-volume, heavily regulated environment. Analysts have to move between fragmented views of a case/customer profile, transaction history, risk indicators to decide whether a flagged transaction warrants a filing. Every missed or mishandled case carries real financial and regulatory consequences. Layered on top of that: Sigma introduces an AI layer into this workflow, which means analysts also need to trust, verify, and override AI-generated suggestions rather than blindly accept them.

The research
We did a market research to understand what solutions our target customers were currently using and did a teardown of our "future" competitors. This included feedai, unit21, verafin etc.
This gave us a bit of an understanding of their features and how they currently meet their customer needs.
Key findings:
86% of our competitors had onboarding systems where they do KYB (Know your business) and KYC (Know your customer)
93% of them had features that helped their clients perform transactions monitoring, AML and fraud detection
75% of them had features that helped clients generate regulatory reports for independent auditing by government bodies
Less than 10% of them had AI features that shows growth insights and natural language to help clients understand data (a gap)

Concept and approach
Based on our research, we had a team meeting and used a priority matrix to select top features that requires less effort to build but has high impact, some of the features we prioritised included:
Case management
Centralizes compliance alerts, investigations, and escalations into a unified workspace. It enables analysts to review agent-drafted case narratives, assign review roles, collaborate across teams, and maintain an audit trail for every resolution.
Transaction monitoring
Analyzes financial flows in real time to detect fraudulent activity and AML anomalies (such as structuring or account takeovers). It uses intelligent alert triage to cluster related transactions, reduce false positives, and prioritize high-risk activity for analyst review.
Risk monitoring
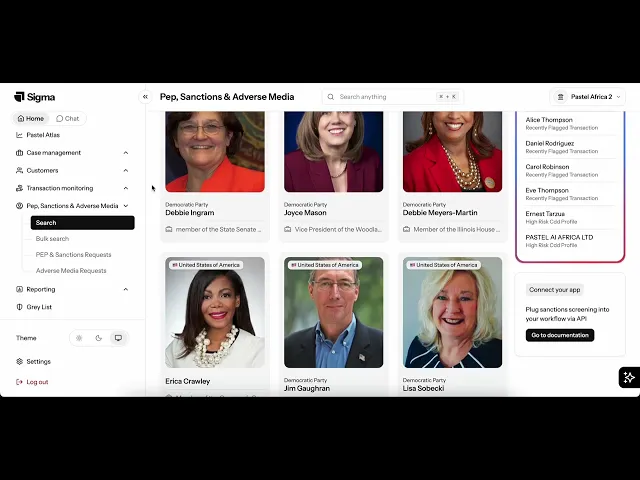
Continuously evaluates entity-level risk throughout the customer lifecycle. It monitors shifts in customer behavior and scans against global watchlists—including Politically Exposed Persons (PEPs), sanctions, and adverse media—dynamically updating risk tiers when vulnerabilities emerge.
Reporting
Automates regulatory compliance filings (such as SAR/STR, CTR, and regional regulatory reports). It aggregates transaction and investigation data to auto-draft filing-ready summaries and ensure exam readiness for banking regulators.
Customer Due Diligence
Standardizes customer onboarding and ongoing KYC verification workflows based on customer classification. It automates identity verification, document collection, and completeness checks, assembling audit-ready CDD packages with clear rationales for approvals or rejections.
Pastel Atlas
A conversational strategic intelligence engine designed for banking executives. It allows leaders to query data across deposits, branches, risk, and customer segments in natural language, automatically surfacing operational trends and generating board-ready summary decks.
Customer Due Diligence
Introduction
In modern banking, standard Customer Due Diligence (CDD) handles the straightforward 80% of accounts. The remaining 20%—cross-border entities, Politically Exposed Persons (PEPs), complex holding groups, and entities flagged for high financial crime risk—demand Enhanced Due Diligence (EDD).
EDD is not a simple checklist; it is an evidentiary investigation. Legacy compliance software forces analysts to trawl through fragmented public registries, paid watchlist vendors, court records, and adverse media portals. The process is slow, high-friction, and cognitively exhausting.
When Pastel set out to build its EDD module, our mission was clear: transform the compliance analyst's role from a manual data scraper into an empowered decision-maker through unified data orchestration, explainable intelligence, and audit-grade reporting.

The research
Spotting Hurdles: The Analyst's Reality
To uncover the daily friction points in financial crime operations, we conducted observational walkthroughs and contextual interviews with AML compliance officers, senior EDD investigators, and risk team leads across partner institutions.
Core Bottlenecks Identified:
1. Context Fragmentation & Tab Overload:
Investigators routinely juggled 8 to 14 open browser tabs and internal tools for a single corporate file. Cross-referencing offshore jurisdictions, commercial registry filings, and negative news resulted in severe cognitive fatigue and lost context.
2. Investigation Anxiety & Omission Risk:
In AML compliance, missing a hidden Ultimate Beneficial Owner (UBO) or an obscure sanctions link carries millions of dollars in regulatory fines. Analysts reported constant anxiety about whether they had checked the 'right' registry version or overlooked an alias.
3. The Reporting Time Sink:
Compiling findings into a defensible, regulator-ready compliance memorandum consumed up to 65% of the total investigation timeline. Analysts spent more time copying, pasting, and formatting audit notes than actually evaluating financial risk.

User Personas: Designing for Diverse Compliance Roles
To build a balanced workspace, we defined two core archetypes representing the day-to-day workflow:
The Forensic Investigator (Senior AML / EDD Analyst):
Prioritizes granular control, transparency of evidence sources, interactive relationship graphs, and quick extraction tools. Focuses on deep unbundling of corporate entities, source-of-wealth tracing, and adverse media verification.
The Compliance Gatekeeper (Team Lead / MLRO):
Prioritizes defensibility, velocity across analyst verdicts, regulatory compliance readiness, and clear audit trails. Focuses on clear decision rationales, override logs, fast secondary reviews and makes decisions on approvals.
Defining the Challenge & Design Sprints
We ran a focused 5-day Design Sprint with product management, engineering, and compliance subject matter experts to tackle two fundamental How-Might-We questions:
"How might we synthesize multi-jurisdiction entity data into a single, cohesive narrative without overwhelming the analyst?"
"How might we present AI-synthesized risk signals with complete evidentiary provenance so analysts can trust and defend every finding?"

Solution Deep-Dive: Crafting Concepts from Chaos
After brainstorming with the entire team, we came up with a straightforward flow that helps create workflows, onboard customers, and customer due diligence checks which generates results for each customer risk rating level, sanctions, adverse media and lots more.
Our guiding design principle became "Explainable by Default": no risk score or flagged connection should ever appear without a direct, one-click link to its verified source material - Hamza
Shots from final designs


Testing, Feedback & Iterative Refinements
We evaluated interactive prototypes through 12 rigorous testing sessions with active AML compliance officers and compliance directors across three banking institutions.
Some Key Refinements Made:
From Abstract Scores to Concrete Risk Drivers:
Our initial prototype featured a 0–100 aggregate risk score with a radar visualization. Analysts found this unhelpful during audits because it obscured the root cause. We pivoted to a Factor-Driven Breakdown that groups risk by category (Location Risk, Transaction Risk, Adverse Media, Cybersecurity Risk) with clear severity chips.
Recurring check Tool:
Testers noted that public web records often vanish or change over time. For example, a low risk individual can become a PEP (Politically Exposed Person) over time. We introduced a feature that checks individuals periodically and keeps records of each check and alerts analysts when a low risk individual becomes high risk.
UI refactoring:
Over time, we had to move things around to meet our client needs, this led to us combining and spliting some of our modules. You can see how sigma currently looks below.
Business Impact & Measurable Outcomes
Deploying the redesigned Enhanced Due Diligence module transformed high-risk operational metrics across pilot banking cohorts:
Metric
Avg. CDD Case Resolution Time
Before Sigma
4.5 Hours
After Sigma
1.2 Hours
+73% Faster turnaround
Metric
Tabs / Tools Used per Case
Before Sigma
10–12 Applications/integrations
After Sigma
1 Unified Platform
Zero tab switching
Metric
CDD Report generation
Before Sigma
Manual
After Sigma
Automatic, based on regulator(s)
Automatic report generation
Key Takeaways & Designer Reflections
1. Trust is the Core UX Metric in Enterprise AI:
In compliance and high-stakes domains, an AI that simply says 'This customer is high risk' is useless. The interface must show why, where the data came from, and how easy it is to verify. Explainability isn't a feature; it is the entire product value.
2. Designing for Skeptical Experts:
Compliance analysts are trained to question every assumption. Designing for them means avoiding decorative visual abstractions in favor of information-dense, high-contrast, scannable data layouts that respect their domain expertise.
3. Speed Comes from Clarity, Not Just Automation:
The largest efficiency gains came not from automating away human judgment, but from eliminating context-switching friction allowing analysts to focus their full cognitive bandwidth on critical risk decisions, analysis and approvals.
Note: As stated earlier, Sigma is a lot more than this, this is just one module, I am open to showing more if you're interested, Thanks for reading!!